Secure shared GPU infrastructure needs both enforcement and evidence
Together, Rafay and Stealthium are addressing a growing requirement for neoclouds, sovereign AI providers, and enterprises: enforcing tenant isolation across shared infrastructure while also producing runtime evidence that those controls are working as intended. As providers increase GPU utilization, support regulated workloads, and move toward shared inference environments where multiple tenants consume the same underlying infrastructure, security has to be delivered by both design and runtime tooling.
This new integration combines multi-tenant GPU governance with runtime visibility at the accelerator layer, helping AI infrastructure operators enforce and demonstrate workload isolation. Now, AI operators can demonstrate that separation to auditors, regulators, and customers.
Rafay governs, Stealthium verifies
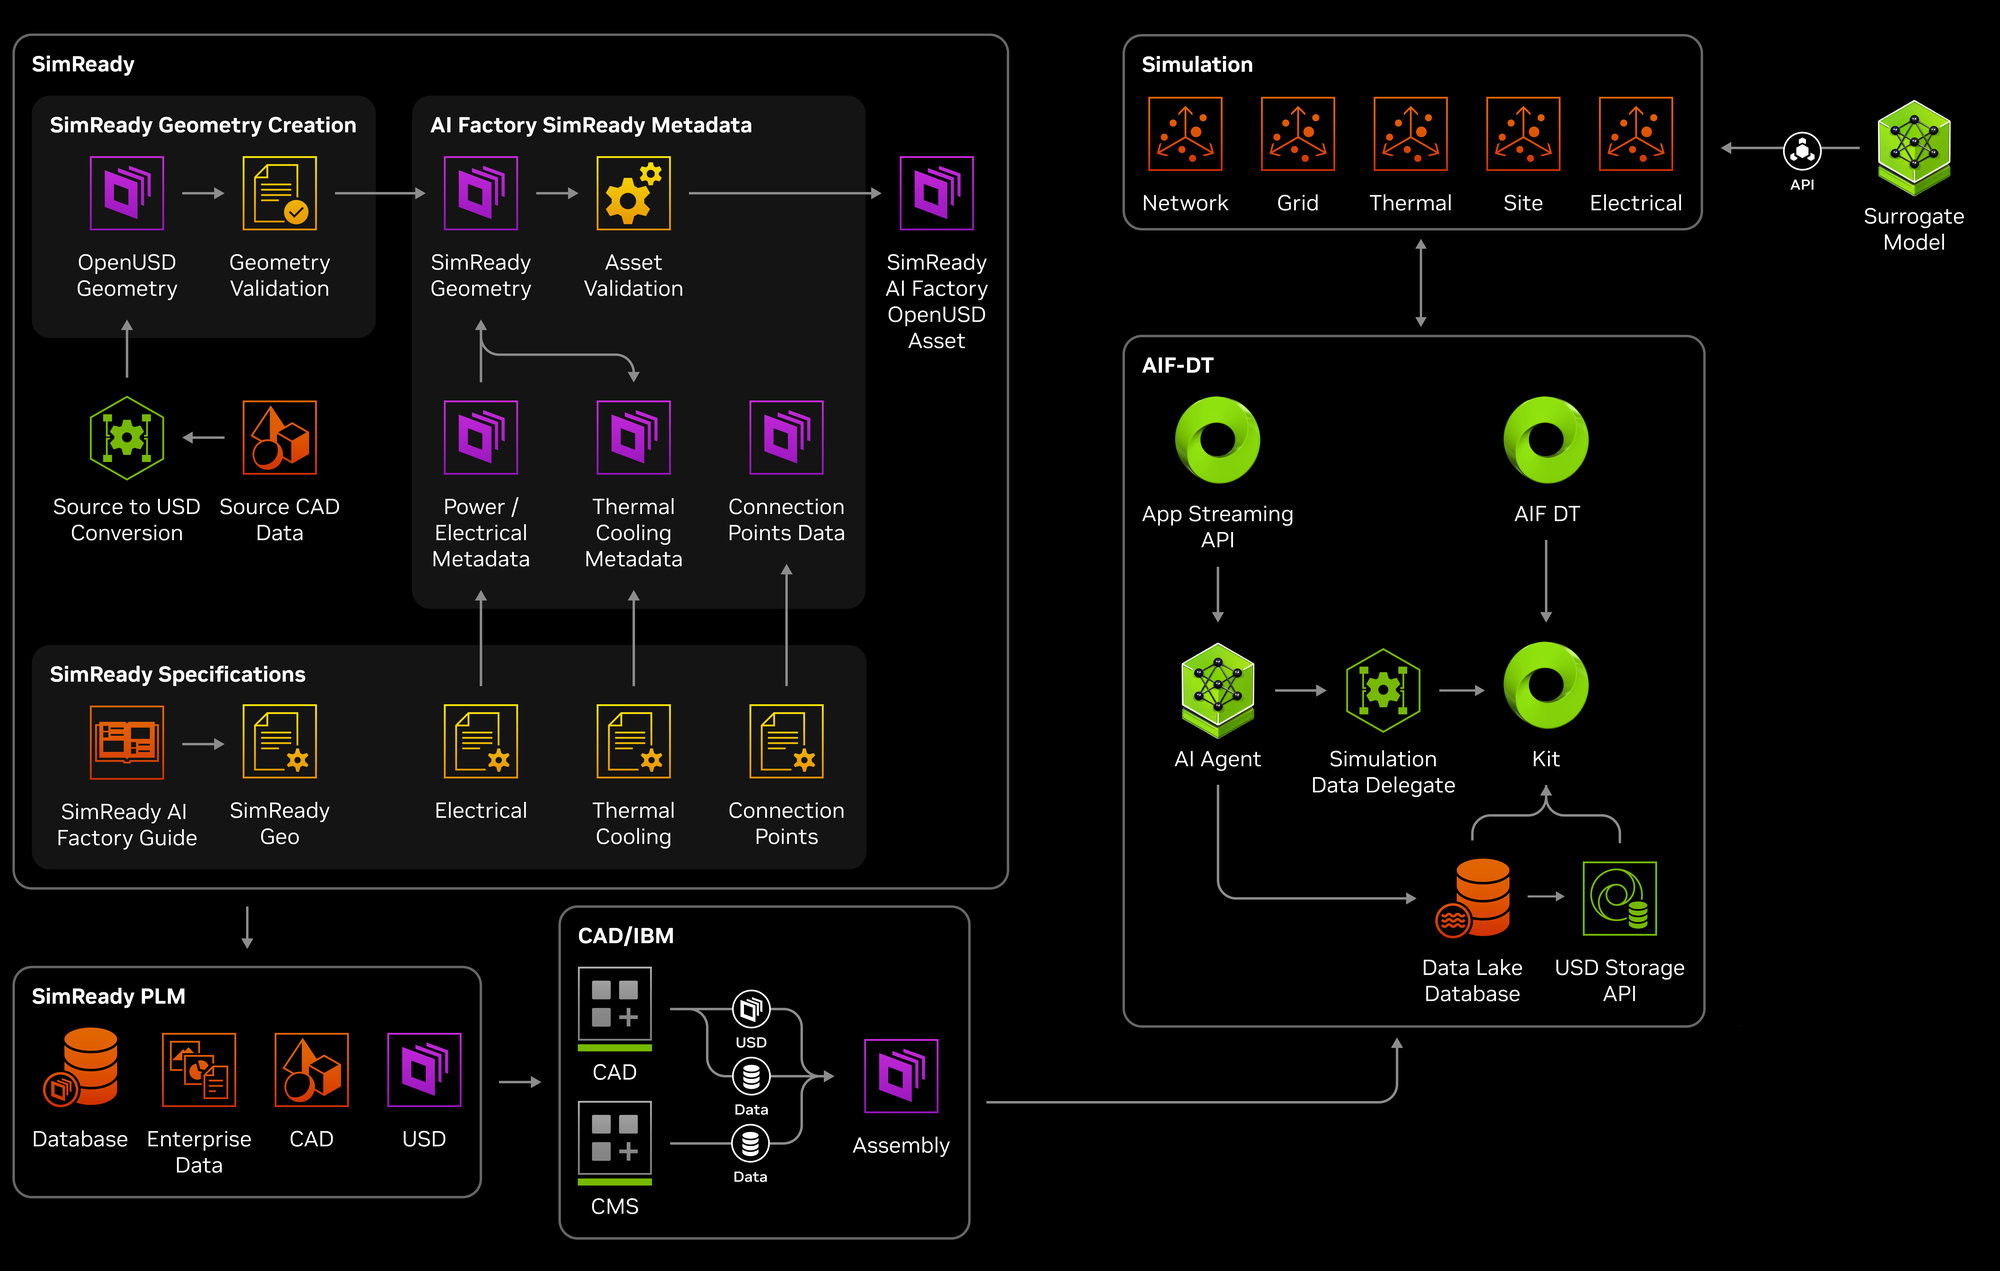
Rafay governs how GPU infrastructure is provisioned, shared, and accessed across tenants. Through multi-tenant compute at scale, the Rafay Platform lets many tenants share one GPU fleet safely, with isolation that runs deep in the stack: virtual clusters and Kata Containers, fractional sharing through MIG and time-slicing, and RBAC, OPA policies, and Zero Trust access per tenant, all governed from a single control plane. Operators manage tenant access, workload placement, cluster isolation, policy enforcement, and GPU sharing from one place, with audit logging by default.
Traditional security and observability tools were largely designed around CPUs, operating systems, and networks, and most of them stop at the accelerator boundary. Stealthium extends observability into that layer. Deployed as a native add-on through a Rafay blueprint, Stealthium instruments NVIDIA GPUs and the CUDA runtime to provide visibility into GPU memory activity, kernel execution, and workload attribution. Operators can see which processes access specific regions of GPU memory, and route detections to the SIEM and SOC systems they already use.
Together, Rafay and Stealthium provide:
- Infrastructure governance: Rafay controls tenant access, policies, workload placement, and shared GPU infrastructure.
- GPU-level visibility: Stealthium observes activity within the NVIDIA GPU and CUDA runtime.
- Runtime verification: Operators can compare configured isolation controls against observed execution.
- Security integration: Stealthium detections map to established security frameworks and feed existing security operations workflows.
Rafay's multi-tenant controls continue to operate independently. Stealthium adds a verification layer for operators who need to evidence what happened on the device."As more tenants share the same GPU infrastructure, operators need to know that the isolation between them actually holds. That is why Rafay and Stealthium are working together, combining Rafay's enforcement across shared infrastructure with Stealthium's runtime visibility into what's happening on each GPU. "Mohan Atreya, Chief Product Officer, Rafay.“
Modern multi-tenancy challenges have extended from clusters to model instances and accelerators. Trustworthy AI requires security and observability by design and via controls. Providing enforcement and observation together is exactly what Rafay and Stealthium are building toward."Ahmed Shosha, CEO and Founder, Stealthium.
The gap between configured and enforced
ASemiAnalysis reportpublished on 30 August 2026, based on security testing across 25 neocloud providers and 32 clusters, documents the gap. Amongst its findings, researchers validated whether a container escape based on a 2025 vulnerability: NVIDIAScape (CVE-2025-23266), was possible across the neocloud providers. (The same vulnerability thatStealthium recently published our analysis and new approach to detection for.) At one provider, that escape opened three separate routes to cross-tenant credential exposure and remote code execution, one of which the researchers demonstrated end to end. Elsewhere, a monitoring API key scoped to a single customer's dashboard carried privilege to read the logs and metrics of every tenant on the cluster, returning metadata belonging to banks, telcos, universities, research institutions, AI labs and, in one case, a national intelligence agency. On another fabric, an isolation partition had been configured correctly but the default partition was left switched on, and a standard diagnostic query returned 532 hostnames belonging to other customers. In each case, there were assumed isolation boundaries that were not performing as intended. What failed was the assumption that the controls on paper were the controls in operation, and there was no operator tooling in place to identify or alert that gap. That is the requirement Rafay and Stealthium are addressing together: enforce isolation across the estate, then observe execution on the hardware itself and confirm the two agree.
“For us, composability is optionality — on multiple vectors.”
Lorem ipsum dolor sit amet consectetur. Amet volutpat id tincidunt enim.
A shared view of verifiable AI infrastructure:
Rafay and Stealthium share the view that secure AI infrastructure requires both enforcement and evidence. Rafay provides the control plane operators use to govern multi-tenant GPU estates. Stealthium adds the runtime layer that shows what actually executed on the hardware. Together, the two companies give operators a way to demonstrate not only which controls are configured, but what those controls did while workloads were running. Learn more about the Rafay Platform's multi-tenancy capabilities, Stealthium, and the Stealthium-Rafay integration.